QCS FOUNDATIONS • UPDATED 3 NOVEMBER 2026
02 / IP addresses, subnets and return paths
Follow subnet decisions, ARP, next-hop headers and the route a reply needs to get home.
Guided analysis · conditional practicals · appliance runtime validation pending
Explore the packet flow — pause, replay or open full screen to inspect headers.
Foundations: guided analysis. Animations are authored examples, not captured appliance results. Practical exercises are conditional drafts: run them only after exact-build licensing, isolation, private management, protected backup and baseline acceptance checks pass. No FortiGate/GNS3 appliance runtime has been validated for this course.
Addresses tell us where; routes tell us the next step
Prerequisite: lesson 1. An IP address identifies an interface in this exercise. A subnet is a group described by a network prefix. In a /24, the first 24 bits are network bits: 10.77.10.10/24 has subnet 10.77.10.0/24 and mask 255.255.255.0. It has usable host addresses .1 through .254; .0 is the network and .255 the broadcast address in this conventional subnet. Do not generalize that last-octet rule to every prefix.
A gateway is a router on the local subnet used to reach another network. A route selects a next hop for a destination prefix. The client sends the remote server’s packet via 10.77.10.1; the server replies via 10.77.20.1. The destination IP stays the remote endpoint; link-layer delivery uses the gateway on each local link. A default route is a fallback, not a requirement here.
Keep these terms beside the explorer
- Prefix
- The network part of an address, written with a bit count such as /24. Here /24 corresponds to mask 255.255.255.0.
- Next hop
- The local router or directly attached receiver selected for the next link. It is not automatically the final IP destination.
- Connected route
- A route associated with an attached, addressed interface. In this baseline FortiGate connects both /24 lab networks.
- Neighbor cache
- Stored mappings between local neighbor IP and link-layer address. A cached entry can avoid a new ARP exchange.
- TTL
- IPv4 Time To Live, a forwarding-lifetime field that decreases when a router forwards the packet. No actual starting value is assumed in this pack.
- Return path
- The route choices needed to carry a reply back to the initiating endpoint. It must work in addition to the forward path.
Build the idea: subnet arithmetic without guessing
An IPv4 address has 32 bits, written here as four decimal octets. The prefix /24 says that 24 bits identify the network. The mask is 255.255.255.0. For this example, 10.77.10.10/24 belongs to 10.77.10.0/24; 10.77.20.10/24 belongs to 10.77.20.0/24. These are different networks. The “first three octets” shortcut is specific to /24; it is not a rule for every prefix.
A route describes where to send traffic for a destination prefix. The client’s route for 10.77.20.0/24 selects gateway 10.77.10.1. That gateway must itself be reachable on the client link. A default route is a fallback for destinations without a more specific match; the experiment needs no Internet default route. If overlapping routes exist, selection requires further checks; the beginner baseline deliberately avoids that complexity.
| Device | Destination network | Required next hop |
|---|---|---|
| LabClient | 10.77.20.0/24 | 10.77.10.1 on the verified client NIC |
| FortiGate | 10.77.20.0/24 | Connected server interface, proposed port3 |
| LabServer | 10.77.10.0/24 | 10.77.20.1 on the verified server NIC |
| FortiGate | 10.77.10.0/24 | Connected client interface, proposed port2 |
Two addresses answer different questions
Client frame: C_MAC → FG_P2_MAC answers “who receives this local Ethernet frame next?” Inside it, IP 10.77.10.10 → 10.77.20.10 answers “which endpoints are communicating?” On the server link, the frame becomes FG_P3_MAC → S_MAC. The IP pair does not become a pair of firewall interface addresses. With ordinary IPv4 routing, TTL decreases as the packet is forwarded; no initial TTL or captured numeric value is assumed here.
On the reply, server IP 10.77.20.10 → client IP 10.77.10.10 travels first inside S_MAC → FG_P3_MAC, then FG_P2_MAC → C_MAC. A permitted session cannot repair a missing route on the server. This is why both directions appear in every acceptance check.
Worked failure analysis
Suppose the request can arrive, but the server’s only route to 10.77.10.0/24 is removed and there is no fallback. The server cannot select the intended remote reply path. The client may wait without a useful response. The decisive lesson evidence is the narrow route change plus the server route lookup and successful restoration—not the timeout alone.
Lab 02: inspect, predict, change one route, restore
Conditional practical: complete the exact-build setup and baseline gates first. Until then, use this as guided analysis and leave observed results blank.
Use this lab only on the disposable server after setup acceptance and a passing HTTP baseline. First collect read-only observations on both endpoints. C_IF and S_IF are worksheet placeholders; substitute the actual verified NIC name only in the two mutation commands.
CLIENT:
ip -br address
ip route
ip route get 10.77.20.10
ip neigh show

SERVER:
ip -br address
ip route
ip route get 10.77.10.10
ip neigh show| Read command | What to read | Common misreading |
|---|---|---|
| ip -br address | Interface name, link state and address/prefix | An UP interface does not prove remote delivery |
| ip route | Destination prefix, next hop, interface, any metrics/tables in the actual setup | Do not delete a route merely because its address looks familiar |
| ip route get | Chosen route, source and next hop for this local lookup | It does not send a ping or HTTP request |
| ip neigh show | Local neighbor entries; cached or unresolved states | A missing entry can simply mean no neighbor traffic has occurred yet |
- Predict the client and server choices before reading the route-get output. Check whether actual selections match the manifest.
- Save the server route listing privately. Confirm the manually created target route is exactly the prefix/next hop/interface shown below, with no extra flags, metric, table or fallback. Otherwise stop for an exact inverse.
- With the helper running, make one fresh client curl request and record the baseline.
- Remove only the verified server remote route. If deletion fails, do not assume the route changed and do not add a duplicate.
- Make one fresh bounded client request; inspect the server route lookup. Record the actual result without inventing an error string.
- After successful deletion, restore the same route, compare with the saved listing, repeat both route lookups and retest HTTP.
SERVER only; replace S_IF with the actual verified server NIC:
sudo ip route del 10.77.10.0/24 via 10.77.20.1 dev S_IF

Exact inverse after successful deletion:
sudo ip route add 10.77.10.0/24 via 10.77.20.1 dev S_IF
sudo requests local administrative authority. ip route del removes the specified runtime route; add restores it. via names the next hop and dev names the interface. No persistent network file is edited. If the inverse reports “file exists,” inspect the table instead of repeating adds. If the original state is uncertain, stop and use the private change ledger; do not remove another route to make a command succeed.
Acceptance: original route choice and HTTP response restored, with no management/default-route or firewall-policy change. Cleanup: leave the known-good route restored and stop only the helper when finished. No global session clear is required.
See the conversation
Detailed diagram: scroll horizontally to inspect full-size labels. The text path below reflows on phones.
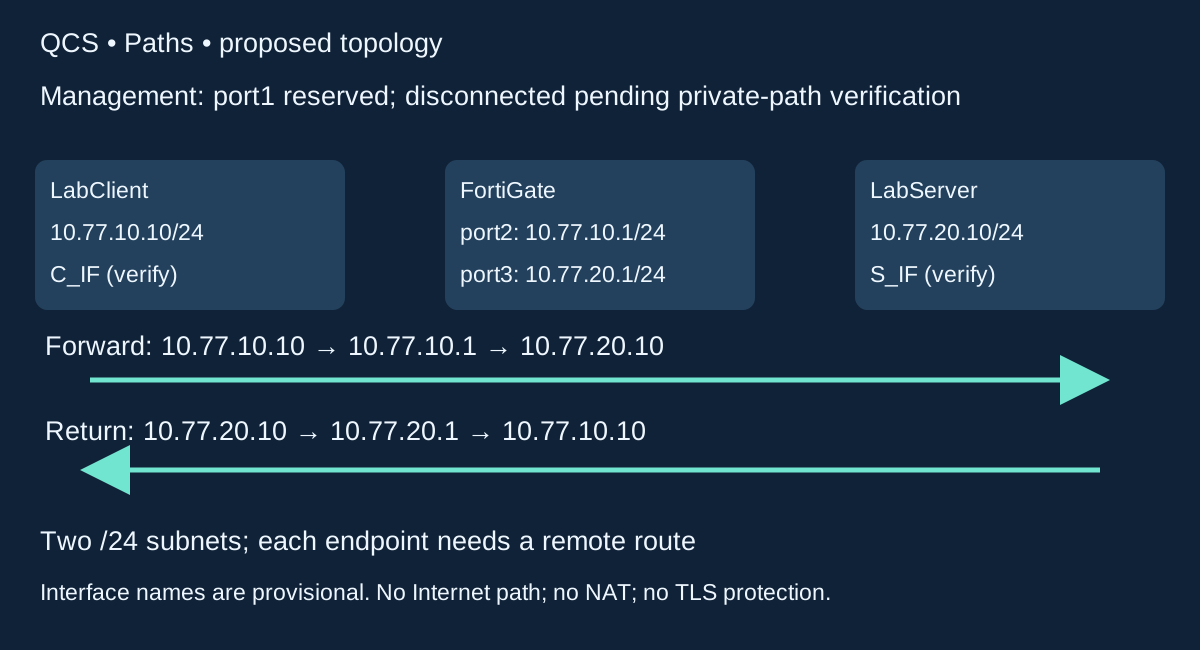
10.77.10.10/24 → local next hop 10.77.10.1 on verified port2.
FortiGate forwards through connected server-side verified port3, 10.77.20.1/24 → server 10.77.20.10.
Server 10.77.20.10 → gateway 10.77.20.1 → FortiGate → 10.77.10.10. The server needs a route to 10.77.10.0/24.
Slow packet explorer • inspect one hop at a time
Start paused. Choose any step, use Previous/Next, or play at your chosen pace. Keyboard: Tab to controls, then Enter/Space; arrow keys work in the native selectors. This is an authored simulation, not a real packet capture.
MAC symbols: C_MAC = client NIC; FG_P2_MAC = client-facing firewall NIC; FG_P3_MAC = server-facing firewall NIC; S_MAC = server NIC. Real names/MACs and build are unverified. ARP cache may already be populated. No NAT or TLS is configured.
10.77.10.10/24
port2 10.77.10.1
port3 10.77.20.1
Full IPs shown in the packet fields
10.77.20.10/24
Concept only; not in lab
Ethernet / local link
IP endpoints / ARP target
Transport header
Decision at this step
Why this happens
What would verify it?
Playing the explorer advances teaching steps only. It sends no network traffic and changes no lab settings. Forward/return lanes summarize packet direction; timing is instructional, not measured latency.
Complete step reference — readable without JavaScript
1. Read the client prefix
Ethernet: No frame sent yet
IP / ARP: Client 10.77.10.10/24; server 10.77.20.10
Transport: Existing permitted TCP conversation excerpt
Decision: /24 means mask 255.255.255.0
Why: For these /24s, compare the first three octets: 10.77.10 differs from 10.77.20. The server is remote.
Evidence: ip -br address reports interface addresses. Do not infer the NIC name from an old screenshot.
2. Select the remote-subnet route
Ethernet: No frame sent yet
IP / ARP: 10.77.10.10 → 10.77.20.10
Transport: TCP 49152 → 8080
Decision: 10.77.20.0/24 via 10.77.10.1 on C_IF
Why: The route selects a next hop on the local subnet. It does not replace the server IP with the gateway IP.
Evidence: ip route get 10.77.20.10 should show via 10.77.10.1 and source 10.77.10.10; output format may vary.
3. Resolve the local next hop if needed
Ethernet: C_MAC → ff:ff:ff:ff:ff:ff
IP / ARP: ARP target: 10.77.10.1
Transport: ARP; no TCP/UDP ports
Decision: Client segment only; cache may already be populated
Why: If uncached, the client broadcasts a request for its local gateway MAC. The following step shows the separate reply; no broadcast is routed to the server network.
Evidence: ip neigh show is read-only. INCOMPLETE/FAILED concerns local resolution; do not assume a policy drop.
4. Receive the local gateway ARP reply
Ethernet: FG_P2_MAC → C_MAC
IP / ARP: ARP reply: 10.77.10.1 is at FG_P2_MAC
Transport: ARP; no TCP/UDP ports
Decision: Reply stays on the client segment
Why: The client can now address a frame to its gateway. A cached entry may make both ARP steps unnecessary. No remote service was tested.
Evidence: Read ip neigh show without flushing the cache. Actual MAC values must be verified privately.
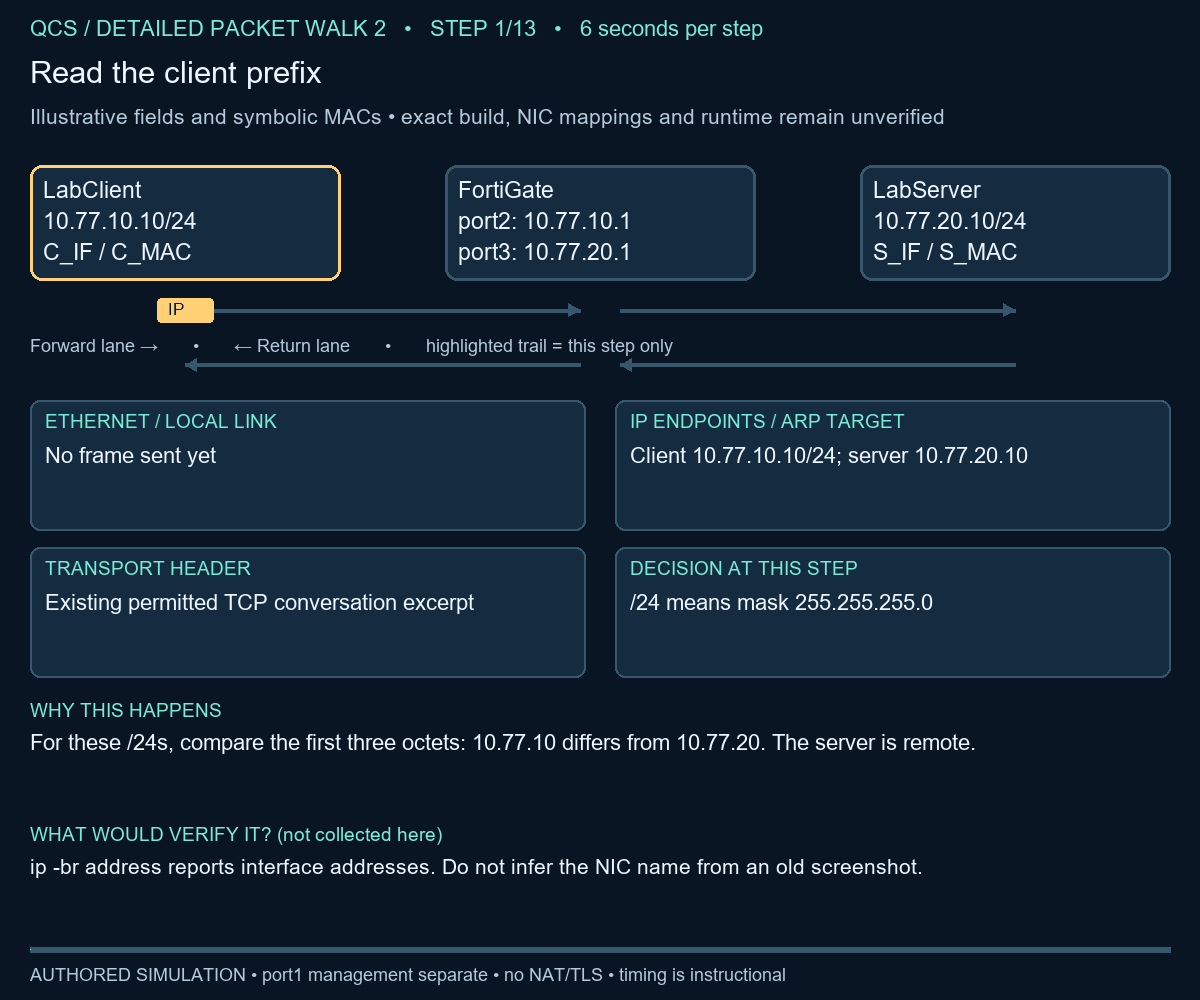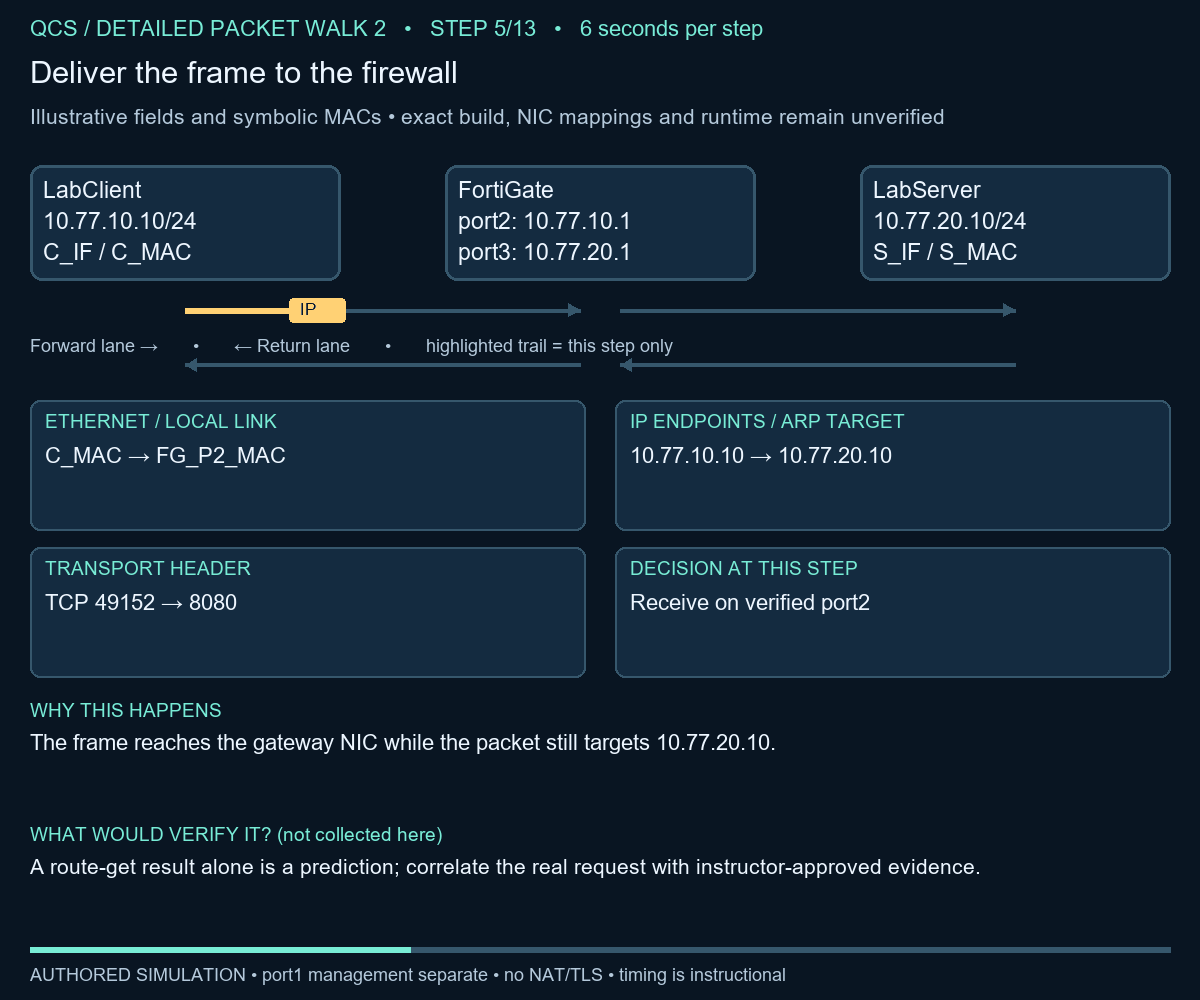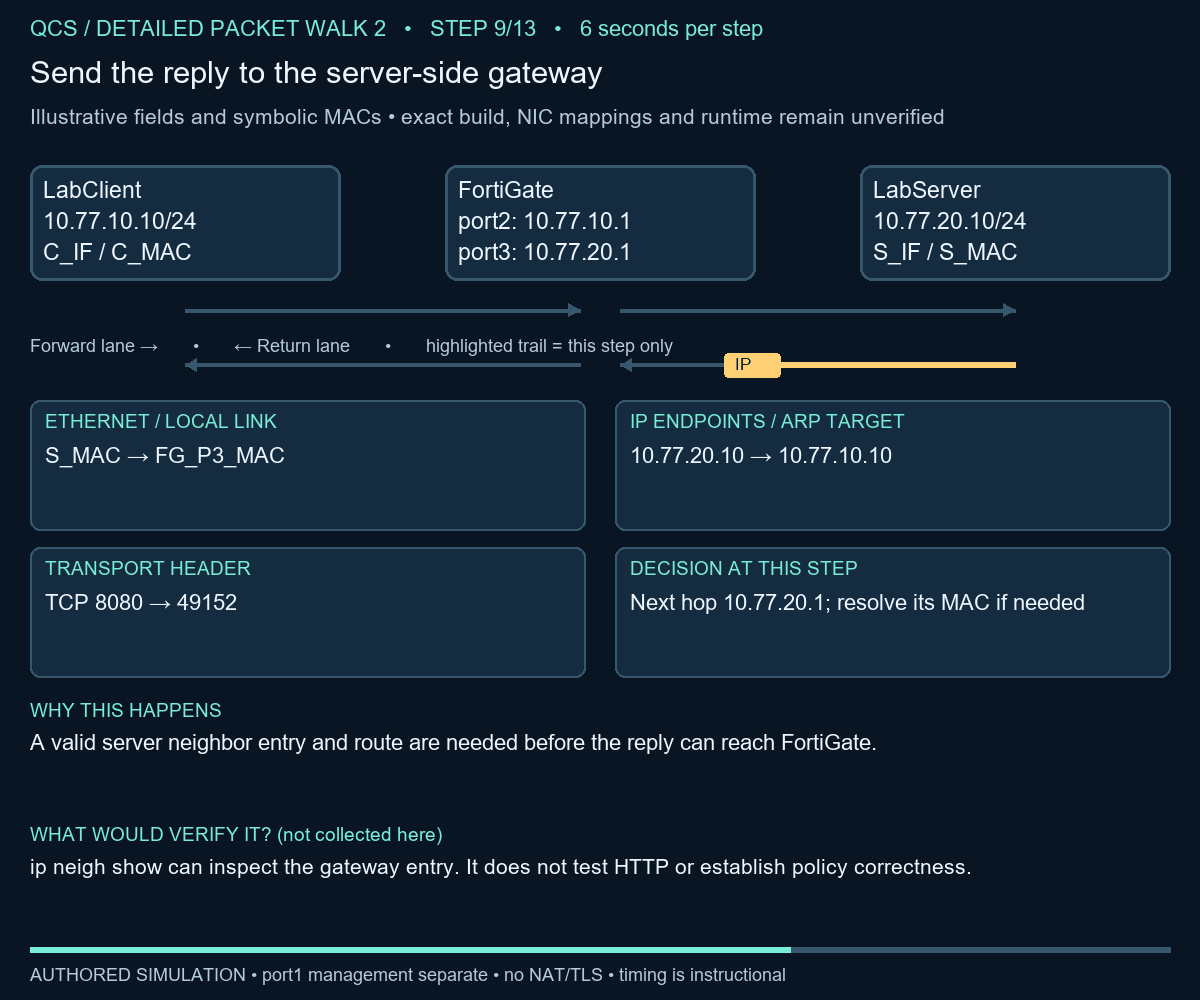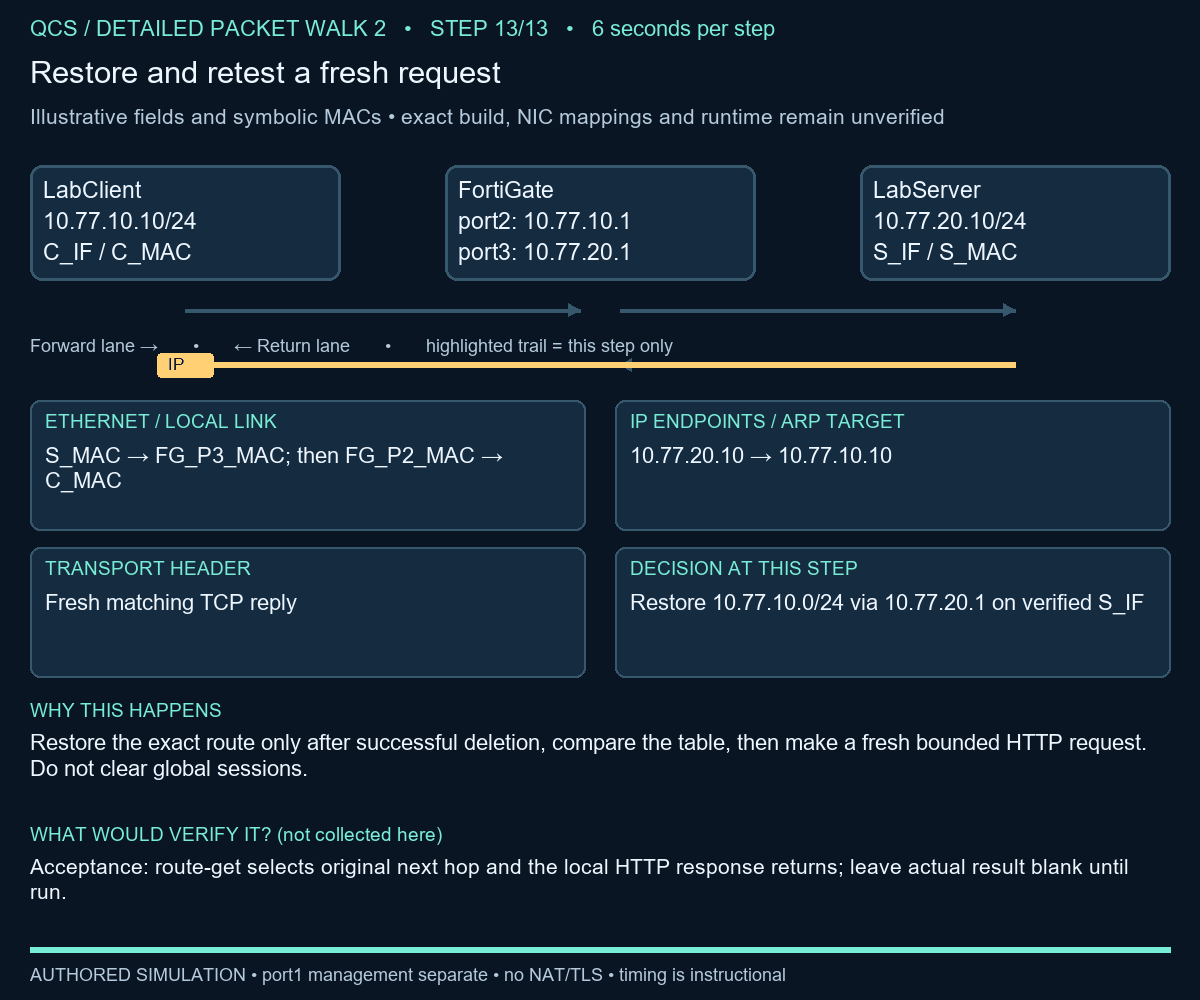
5. Deliver the frame to the firewall
Ethernet: C_MAC → FG_P2_MAC
IP / ARP: 10.77.10.10 → 10.77.20.10
Transport: TCP 49152 → 8080
Decision: Receive on verified port2
Why: The frame reaches the gateway NIC while the packet still targets 10.77.20.10.
Evidence: A route-get result alone is a prediction; correlate the real request with instructor-approved evidence.
6. Route toward the connected server subnet
Ethernet: Replace ingress Ethernet header for the next link
IP / ARP: 10.77.10.10 → 10.77.20.10
Transport: Same TCP ports; NAT off
Decision: Connected 10.77.20.0/24 through port3; matching permit required
Why: Routing selects a path; access policy decides whether this forwarded flow may use it. Neither proves the service is running.
Evidence: Instructor checks connected route and narrow policy. This panel does not claim an exact internal FortiOS processing sequence.
7. Forward on a new Ethernet link
Ethernet: FG_P3_MAC → S_MAC
IP / ARP: 10.77.10.10 → 10.77.20.10
Transport: TCP 49152 → 8080
Decision: Source/destination IPs stay; IPv4 TTL decreases when routed
Why: TTL limits forwarding lifetime; its actual initial value is not assumed. MAC headers change at the router, while endpoint IPs remain the same with NAT disabled.
Evidence: Optional guided trace comparison: same endpoint tuple, new link MACs. No numeric TTL or MAC here is captured evidence.
8. The server chooses the reply route
Ethernet: No reply frame until route/neighbor selection
IP / ARP: 10.77.20.10 → 10.77.10.10
Transport: TCP 8080 → 49152
Decision: 10.77.10.0/24 via 10.77.20.1 on S_IF
Why: The server must reach the client subnet independently of the route used by the request.
Evidence: Server: ip route get 10.77.10.10. A successful local self-ping cannot verify this path.
9. Send the reply to the server-side gateway
Ethernet: S_MAC → FG_P3_MAC
IP / ARP: 10.77.20.10 → 10.77.10.10
Transport: TCP 8080 → 49152
Decision: Next hop 10.77.20.1; resolve its MAC if needed
Why: A valid server neighbor entry and route are needed before the reply can reach FortiGate.
Evidence: ip neigh show can inspect the gateway entry. It does not test HTTP or establish policy correctness.
10. Forward the matching reply to the client
Ethernet: FG_P2_MAC → C_MAC
IP / ARP: 10.77.20.10 → 10.77.10.10
Transport: TCP 8080 → 49152
Decision: Allowed session; connected client subnet via port2
Why: The return Ethernet frame is built for C_MAC. No reverse allow-any rule is needed merely for this matching reply.
Evidence: Correlate time and reversed IP/port tuple with the original request.
11. Introduce only the owned route fault
Ethernet: No successful remote reply frame
IP / ARP: 10.77.20.10 → 10.77.10.10
Transport: Reply cannot use the removed remote route
Decision: Remove only the exact manually created server route; no fallback route
Why: The lesson fault is not an interface shutdown or firewall change. If other metrics/tables/flags exist, stop and prepare an exact inverse first.
Evidence: Record baseline before sudo ip route del. Do not remove a default route, management route or unrelated prefix.
12. Locate where the reply stops
Ethernet: No valid next-hop selection for the remote client
IP / ARP: 10.77.20.10 → 10.77.10.10
Transport: No delivered reply; outcome depends on local stack
Decision: Stop at server route lookup, before firewall ingress
Why: A curl timeout cannot locate the fault. Here the controlled change and failed server route lookup support the return-route hypothesis.
Evidence: One attempt, then route-get, baseline comparison and known listener check. Restore before exploring another hypothesis.
13. Restore and retest a fresh request
Ethernet: S_MAC → FG_P3_MAC; then FG_P2_MAC → C_MAC
IP / ARP: 10.77.20.10 → 10.77.10.10
Transport: Fresh matching TCP reply
Decision: Restore 10.77.10.0/24 via 10.77.20.1 on verified S_IF
Why: Restore the exact route only after successful deletion, compare the table, then make a fresh bounded HTTP request. Do not clear global sessions.
Evidence: Acceptance: route-get selects original next hop and the local HTTP response returns; leave actual result blank until run.
Slow packet film: 13 steps, six seconds per step (78 seconds total). Pause to inspect the headers, or use the explorer above at 10/15 seconds per step. Film timing is instructional; it is not measured network latency.
No autoplay. Use native pause or leave the static diagram visible. Reusable GIF download. The static diagram and caption are the reduced-motion alternative; GIFs are not embedded.
Practical 02 • inspect and remove one owned route
Conditional practical: complete the exact-build setup and baseline gates first. Until then, use this as guided analysis and leave observed results blank.
On each Ubuntu console, ip -br address lists interface names and addresses; ip route lists routes. Do not assume eth0. Record the verified client interface as C_IF and server interface as S_IF in the private lab worksheet; these are placeholders, never literal commands.
CLIENT read-only:
ip -br address
ip route
ip route get 10.77.20.10

SERVER read-only:
ip -br address
ip route
ip route get 10.77.10.10
ip route get asks Linux which path it would use; it does not send a service request. Expected client choice: via 10.77.10.1 and the verified client NIC, source 10.77.10.10. Expected server choice: via 10.77.20.1, source 10.77.20.10.
- Start from a passing HTTP baseline with the helper running. Save both route listings.
- Only if the server has exactly the manually created route shown below, with no fallback route, remove it. Replace S_IF with the real interface name. If the route has other metrics, tables or flags, stop and prepare an exact inverse instead.
- Run one bounded client curl from lesson 1. Expected failure or missing reply; corroborate the server route-get result. Do not call this a firewall block.
- Restore exactly the removed route; repeat both route-get and HTTP checks. Acceptance: original route and HTTP 200 restored. No persistent network files changed.
SERVER only, after baseline check; replace S_IF:
sudo ip route del 10.77.10.0/24 via 10.77.20.1 dev S_IF

Exact inverse, same console:
sudo ip route add 10.77.10.0/24 via 10.77.20.1 dev S_IF
sudo authorizes a local administrative action. del removes this one prefix/next-hop route; add restores it; dev names the verified NIC. If deletion fails, do not add a duplicate route. These temporary commands affect only the disposable server’s runtime route table.
Diagnosis, cleanup and practice
Check at most: interface address/up state, route-get choice, then the known helper/policy baseline. Stop if a default route or unexpected NIC appears. Cleanup is the exact route restoration above, followed by the baseline comparison; stop the helper only after testing. Practice: why can a request reach the server while its reply fails? The forward and return route choices are separate. Does a ping to 10.77.10.10 from that same client test the firewall? No. Which prefix holds 10.77.20.10/24? 10.77.20.0/24.
Evidence and boundaries
Use the evidence worksheet. Write prediction before observation; record time, exact command, endpoints, policy ID if available and a redacted result. Leave actual-result cells blank until tested. Never paste passwords, license files, serials, full configurations or recovery backups into the preview.
Stop after one failed attempt and up to three focused checks. A timeout alone is inconclusive: service, route, host filtering or firewall policy may be responsible. Restore the stated fault before trying a different hypothesis.
More practice • explain before revealing the answer
Is 10.77.20.10 local to 10.77.10.10/24?
No. The two addresses have different /24 network prefixes.
Does the gateway replace the destination IP?
No. It is the next local link receiver; the remote destination IP remains the server.
Which MAC headers carry a reply across the two links?
S_MAC → FG_P3_MAC, then FG_P2_MAC → C_MAC.
Why inspect ip route before a route deletion?
To verify ownership and capture the exact original prefix, next hop, NIC and any extra attributes.
What if deletion fails?
Do not assume the fault was introduced; inspect the table and do not add a duplicate inverse.
Does route-get prove HTTP delivery?
No. It predicts local routing selection; the application request and response are separate evidence.
QCS Institute · FortiGate foundations
Work through the explanation, inspect each header, then use the lab acceptance checks.