Cloud
Cloud Network Services
Design and secure AWS VPC, Azure VNet, Google Cloud VPC, site-to-site VPN, routing, private access, and public exposure.
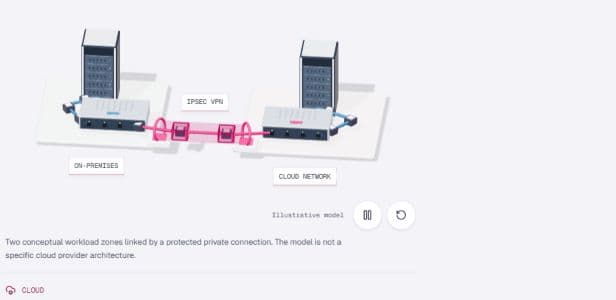
Two conceptual workload zones linked by a protected private connection. The model is not a specific cloud provider architecture.
- 01Current stateMap the environment and pressure.
- 02Authorized scopeAgree access, impact, and owners.
- 03Engineering workOperate, change, or remediate.
- 04Verified handoffDocument evidence and next controls.
Best fit
Who this service is for
Teams moving workloads to cloud or connecting offices, users, vendors, and applications across hybrid environments.
The work focuses on route intent, exposure, segmentation, logs, identity-aware access, and performance instead of isolated cloud settings.
Outcomes to plan for
- Cloud visibility
- Safer public exposure
- Cleaner routing
- Cost-aware connectivity
Operational triggers
Choose this service when these signals appear.
Scope
What we inspect, operate, or change.
Agree the systems, access permissions and change boundaries before work starts. The engagement scope determines which activities are included.
- VPC/VNet review
- Route and subnet mapping
- Security group/NSG review
- Hybrid VPN design
- Flow log and exposure review
Deliverables
What remains with your team after the work.
- Cloud network map
- Exposure inventory
- Segmentation recommendations
- Connectivity risk notes
- Cloud readiness backlog
FAQ
Questions to resolve before work begins.
Can QCS review an existing cloud network?
Yes. The review can inspect VPC/VNet structure, subnets, routes, security groups, VPNs, public IPs, load balancers, flow logs, and cloud connectivity risks.
Does cloud network work include security?
Yes. Cloud networking and security overlap through routes, public exposure, segmentation, private access, security groups, logging, and identity-aware access.
Request review
Discuss cloud network services.
Tell us about your environment, the issue or project, and the outcome you need. Do not include passwords or sensitive configuration details.